 If the only time you connect with your IT provider is when there is an issue or a renewal on the table, you are missing a critical opportunity to strengthen your business.
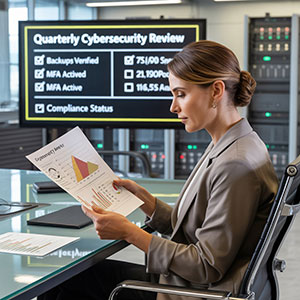
Cybersecurity is not a set-it-and-forget-it solution. It requires regular attention and adaptation. A quarterly cybersecurity risk review is essential for identifying vulnerabilities, ensuring compliance, and improving your overall security posture.
Here are seven questions every business leader should ask during a quarterly review. These questions will help you hold your IT partner/department accountable and keep your operation secure.
- What Is Our Current Risk Exposure?
Your business cannot defend against what it cannot see. Each quarter, ask your IT provider:
- Have any new vulnerabilities been discovered in our systems?
- Are our defenses still effective against phishing, ransomware, and insider threats?
- Are endpoint protection, access controls, and monitoring tools functioning as expected?
You need a clear, plain-language understanding of your risk level today.
- Are Our Backups Verified, Secure, and Ready for Recovery?
Backup systems are only as good as their last successful test. In a quarterly review, make sure to ask:
- When was our last backup restoration test?
- Are we backing up all critical data, including operational technology?
- Are backups encrypted, stored off-site or in the cloud, and protected from cyber threats?
Reliable backups are essential for both recovery and compliance.
- Are Our Employees Following Security Best Practices?
Your team is either your greatest defense or your biggest vulnerability. Quarterly, review:
- Have there been any incidents linked to employee behavior?
- Do we need a refresher phishing simulation or awareness training?
- Is multi-factor authentication active across all user accounts?
Human error is one of the leading causes of cyber incidents. Ongoing training helps reduce that risk.
- Are We Still Compliant With Required Cybersecurity Standards?
Compliance is not static. If you are working toward CMMC, NIST SP 800-171, or vendor-specific requirements, ask:
- Are we meeting all relevant compliance requirements?
- Have there been updates to security frameworks or audit criteria?
- Are our logs, policies, and reports ready for review if requested?
Non-compliance can result in contract loss, failed audits, or insurance denials.
- What Security Incidents or Near Misses Occurred This Quarter?
Your IT provider should be tracking everything, not just major breaches. Ask:
- Were there blocked phishing attempts, unauthorized login attempts, or endpoint anomalies?
- How quickly were incidents detected and addressed?
- Have we conducted root cause analysis on any alerts?
These discussions help identify weak spots and improve incident response plans.
- What New or Emerging Threats Should We Be Watching?
Threat actors do not wait for you to catch up. Ask:
- Are there industry-specific threats we are not yet defending against?
- Are new vulnerabilities emerging in our operating systems, IoT devices, or industrial controls?
- Are there tools or security practices we should consider for the coming quarter?
Staying ahead of trends is part of reducing long-term risk.
- What Changes Should We Make Before the Next Quarter?
Your cybersecurity strategy should adapt based on what is learned. Finish each review by asking:
- Are there software updates, policy changes, or hardware replacements needed?
- Do we need to make adjustments to access controls or endpoint configurations?
- What should be prioritized for remediation or upgrade?
A proactive roadmap avoids future surprises and supports long-term resilience.
Not Having These Conversations? That’s a Problem.
If your current provider cannot confidently answer these questions, or if they are not initiating quarterly risk reviews at all, it is time to reassess the partnership.
Cyber threats are evolving. Compliance requirements are tightening. Your business deserves more than reactive support.
At Watchdog Cyber, we help manufacturers in Michigan maintain operational security and compliance with structured, proactive quarterly reviews.
Schedule a Security and Compliance Risk Assessment to understand where you stand and what to fix before it costs you a contract.
Click here to book your assessment.
#CybersecurityReview #QuarterlyRiskReview #ManufacturingSecurity #MSSP #ComplianceAudit #OperationalSecurity #MichiganManufacturing #RiskAssessment #CyberSecurity #WatchdogCyber